Massive Supply Chain Attack on LiteLLM Exposes Over 2,500 Organizations and Critical Data
A significant cybersecurity incident has come to light involving a supply chain attack on the open-source LiteLLM framework, leading to the potential exposure of sensitive data from more than 2,500 organizations globally. This breach, described as the largest supply-chain attack targeting AI infrastructure so far in 2026, resulted in the theft of a massive 153GB archive of credentials and other critical information. The attack, orchestrated by the cybercriminal group TeamPCP in March 2026, initially exploited a compromise in Trivy, a widely used open-source vulnerability scanner. LiteLLM's automated build pipelines installed the compromised Trivy version, allowing attackers to steal PyPI publishing tokens.
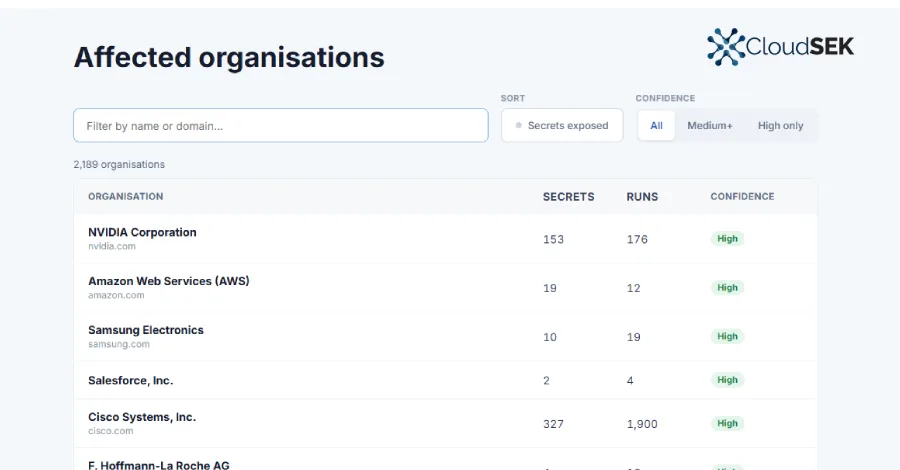
Using these stolen tokens, TeamPCP published two malicious versions of LiteLLM (1.82.7 and 1.82.8) to the Python Package Index. Although these malicious versions were live for only about 40 minutes, the brief window was sufficient for the attackers to compromise approximately 434,000 CI/CD pipelines, leading to widespread data exposure. The stolen data includes cloud keys, SSH keys, Kubernetes tokens, and database passwords, affecting corporate domains such as AWS, Samsung, Cisco, and Salesforce. This incident underscores the escalating threat of supply chain attacks, where a single vulnerability in an upstream component can ripple through numerous downstream users, highlighting the critical need for robust cybersecurity measures across the entire software development lifecycle.